How I Was Able To Takeover All User Account And Admin Panel

Hi everyone, This is my last write-up of 2018, so 6 months ago I got the invite from a Hackerone private program, the program has a huge scope, so currently I am focused on that single program. Found a subdomain let say abc.example.com (As it a private program so we will be using example.com instead of the original domain)
So let's start
The vulnerability was a pretty straightforward IDOR
So, the website uses sso for authentication, after successful authentication its redirect back the subdomain abc.example.com
after exploring the functionality, I found its a very basic site where no option to edit your own account even, many static pages and some third party links.
so after that, I navigate to the https://abc.example.com/robots.txt and found lots of hidden directories are there, like /admin, /user
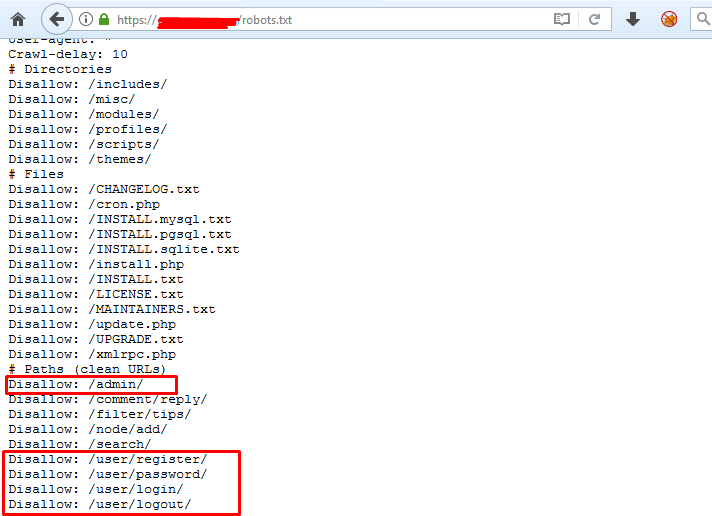
so quickly I navigate to the directory /user it redirected me to https://abc.example.com/user/16397/edit
that page provides functionality like change password, change email id, change address, add an address
Next, I just change the value to 16390, then it's redirected me to the user edit option of the user which associated with 16390 userid
Then I created another test account to verify the issue, I am successfully able to change password and email of the user
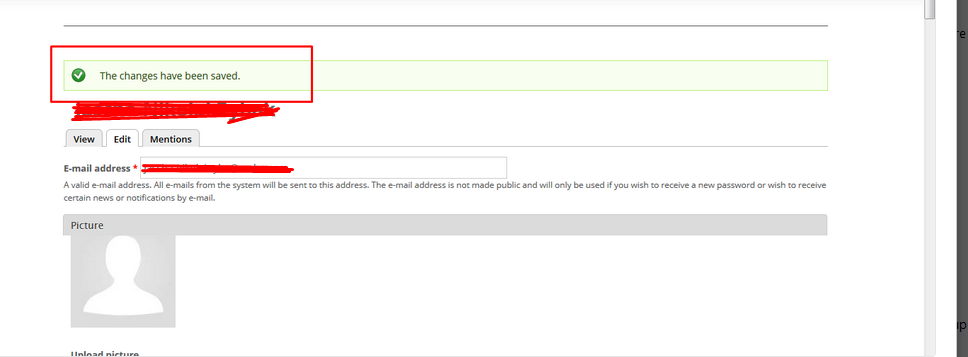
Then I thought to give a try for admin panel takeover, so iIvisited to https://abc.example.com/user/1/edit
its redirected to me to the portal admin panel where i can change admin password email

So at that point ,i can able to takeover all user account by changing the userid value as all are sequential and admin panel too .
After 4 days they fixed the issue and got a nice bounty and bonus , that helped me to fullfill my last 2018 goal.

Thanks for reading, any suggestion feedback are welcome
About the author
Security Engineer
Comments
Join the discussionNo comments yet. Be the first to comment.